A keychain that also works outside Apple's ecosystem
Compare Apple Keychain (iCloud) and VaultKeepR by encryption, storage, access, and export format. The notes below distinguish supported settings and account models.
The short answer
- Switch if you use a Windows or Linux machine alongside your iPhone.
- Switch if you want an export you can read without Apple hardware.
- Stay if everything you own is Apple and you trust iCloud Advanced Data Protection.
macOS exports CSV from System Settings, Passwords. Import locally. Migration steps
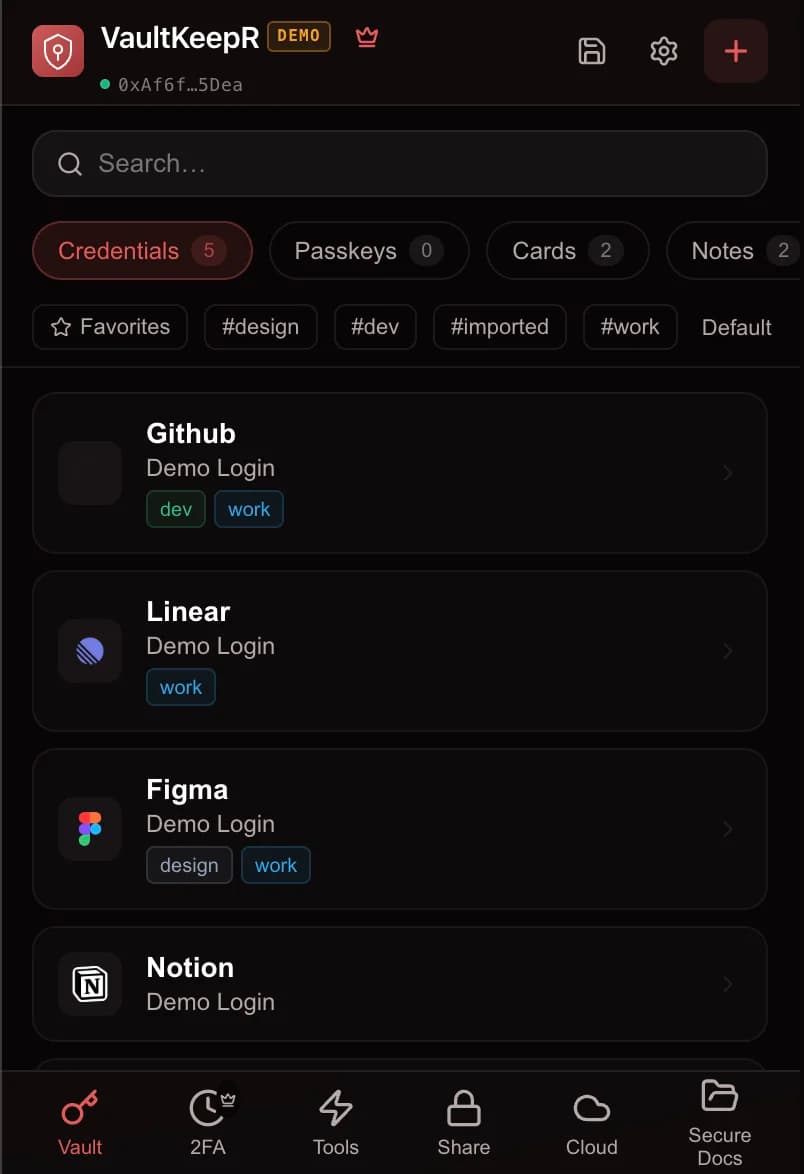
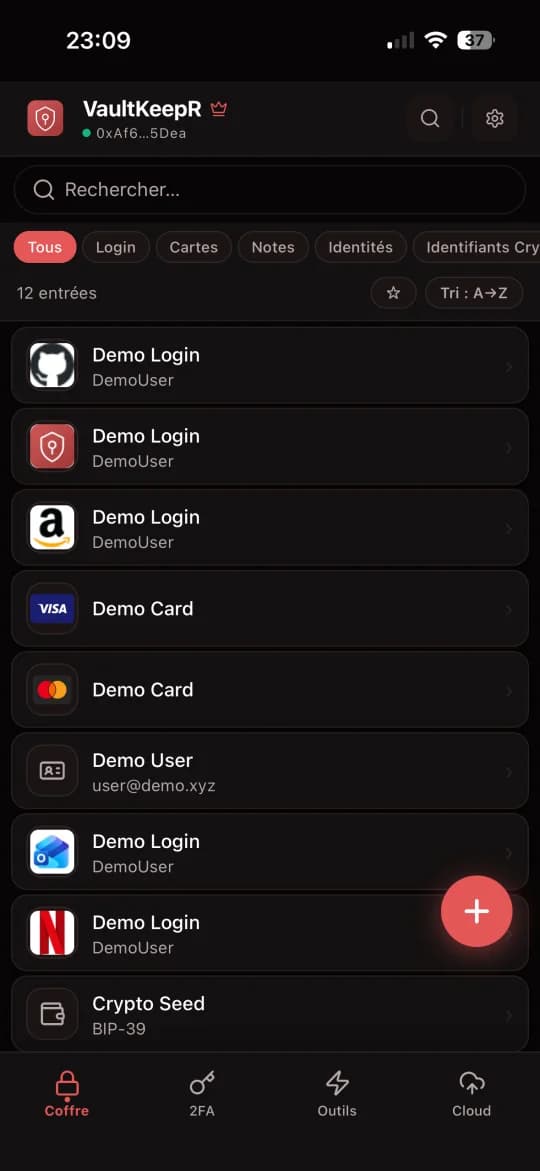
Swipe or scroll sideways to see all columns. With a keyboard, focus the table and use the left and right arrow keys.
| Comparison | VaultKeepR | Apple Keychain (iCloud) |
|---|---|---|
| Encryption and key derivation | XChaCha20-Poly1305 + Argon2id | AES-256-GCM locally; end-to-end encrypted iCloud Keychain sync |
| Storage location | Local encrypted vault / IPFS sync | Device keychain / encrypted iCloud Keychain sync |
| Access & Auth | Password + Secret Key / compatible passkey | Device passcode / Face ID / Touch ID; Apple Account for iCloud |
| Open-source license | Yes | No |
| Public implementation for review | Public SDK; not an external security audit | No |
| Pricing | Free local vault and IPFS sync; Premium extras | Included with supported Apple devices |
What actually changes when you leave Apple Keychain (iCloud)
iCloud Keychain is deeply integrated and almost invisible: passwords sync through iCloud, autofill happens in Safari and in apps, and passkeys are stored in the same place as passwords. With Advanced Data Protection enabled, the keys are end-to-end encrypted and Apple cannot read them. The limitation is the ecosystem. There is no Windows or Linux client, and the vault is tied to an Apple ID rather than to a file or a device you control.
Exporting is a macOS-only operation, through System Settings then Passwords, and it produces a CSV. Do it on the Mac, copy the file straight into the import screen, and delete it. Passkeys and verification codes do not come across, and shared password groups are not represented. If everyone in your household is on Apple hardware, the integration is worth more than the portability.
Why users choose Apple Keychain (iCloud)
- • Native Apple password and passkey integration
- • End-to-end encrypted iCloud Keychain sync
- • Device biometric unlock
What to check with Apple Keychain (iCloud)
- • Apple Account for iCloud sync
- • Platform support differs outside Apple devices
- • Review keychain recovery before replacing your devices
Encryption and key derivation
Apple documents AES-256-GCM protection for local keychain items and end-to-end encryption for iCloud Keychain synchronization. This is not a generic master-password PBKDF2 vault. Keychain protection and unlock requirements depend on the operating system and item class.
VaultKeepR encrypts vault contents with XChaCha20-Poly1305 and uses Argon2id for password-based key derivation. Argon2id raises the cost of offline guessing, but protection still depends on the unlocking secret, KDF parameters, and device security.
Vault copies and remote availability
Keychain items live on supported devices, with optional synchronization through Apple's servers. iCloud Keychain synchronization is end-to-end encrypted. Its separate recovery service should not be treated as proof that Apple can read the passwords it syncs.
VaultKeepR keeps an encrypted local vault and syncs an encrypted vault blob through IPFS. Shamir recovery fragments are separate from that blob. Remote access depends on gateways, continued pinning, and the configured storage services, including S3 backup. Keep a local copy or export that you can unlock.
Account and unlocking methods
Device passcodes and supported biometrics control local access. An Apple Account is used for iCloud Keychain sync and recovery. Check the recovery prerequisites and support on the platforms you plan to use.
VaultKeepR does not require an email-based vault account. Unlock methods depend on the app and compatible hardware. Removing email registration does not prevent phishing, compromised-device access, or metadata linkage.
Recovery and independent backups
The local vault and IPFS sync are free. Shamir 3-of-5 fragmented recovery is part of Premium. Set it up before losing access; recovery requires the necessary fragments and recovery information.
If you lose the unlocking secrets without a usable recovery setup or another accessible vault copy, you can lose access to the vault. An email reset cannot recreate a lost encryption key. Test recovery and keep independent backups before relying on them.
Read the full guide: What is a Zero-Knowledge Password Manager?
Sources and scope
Facts checked on . Features depend on the client, format, KDF settings, and account model. Pricing can change by region, billing period, and promotion. USD prices are not converted to EUR here.
VaultKeepR references: Architecture, threat model, recovery, pricing.
Frequently asked questions
How can I transfer my passwords from Apple Keychain (iCloud)?
Can I access my passwords offline?
Is VaultKeepR really free?
Does VaultKeepR work with passkeys and biometrics?
Where is my data actually stored?
Other comparisons
Switching managers is also a good time to close the accounts you no longer use. Our guides cover how to delete accounts on 15 major services.
Try a local-first vault
Use the transfer method for Apple Keychain (iCloud) above, then verify the imported entries. Keep a backup and your unlocking material available.